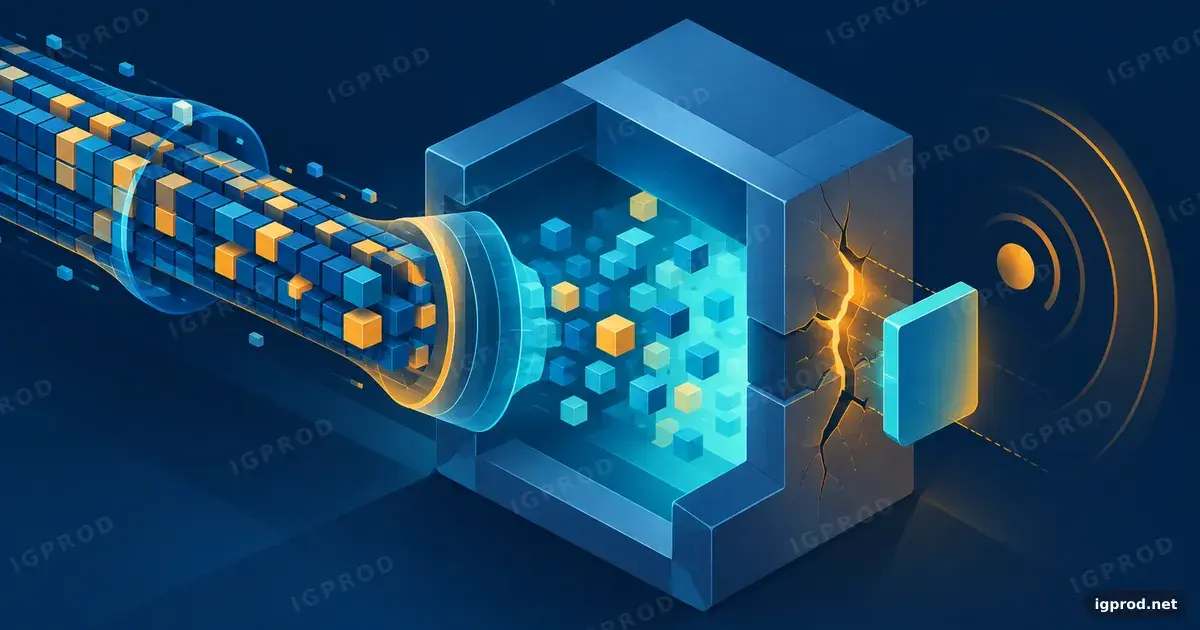
The GitHub Advisory Database published GHSA-9v8h-qqgm-4m35 on October 22, 2026, confirming that an out-of-bounds write in the Brotli C decoder affects the PyPI brotli package. The flaw, tracked as PYSEC-2026-4322 and nicknamed "Node2Shell," triggers when the decoder processes a crafted Brotli stream.
Identify the affected PyPI package
The advisory states that the PyPI Brotli package is subject to the same decoder flaw. Applications that install brotli from PyPI and decompress untrusted data are exposed. The decoder runs automatically when HTTP libraries such as urllib3, requests, httpx or aiohttp receive a Content-Encoding: br response, even if the client did not advertise Brotli support in the request headers.
Check which version is installed in the environment your application runs. The commands below inspect a local or virtual environment, but they do not confirm which version a deployed application process has loaded:
pip show brotli
or in a uv-managed project:
uv pip list | grep brotli
If your application fetches external URLs, accepts file uploads, or uses connectors that request user-configured resources, trace whether those paths can reach the Brotli decoder. HTTP libraries decode br responses automatically when the package is installed, and a remote server can send a Brotli body even when the request asks only for gzip or deflate.
Understand the decoder vulnerability
The flaw is an out-of-bounds write in the C implementation of the Brotli decoder. When the decoder reads a specially crafted stream, it writes beyond the allocated buffer. Web applications are reachable if they use HTTP libraries that auto-decode Brotli responses; a malicious or compromised server can send a Content-Encoding: br header with a crafted body, and the decoder processes it without application involvement. Command-line tools and batch processors that accept user-supplied compressed files are similarly exposed.
Review Onyx's dependency update
The Onyx project opened CVE alert issues for PYSEC-2026-4322 across its release branches. The maintainers report that they pinned brotli to version 1.2.1 in their root pyproject.toml and note that Onyx never calls brotli directly, yet is affected because urllib3 and requests decode Content-Encoding: br responses automatically when the web connector or other URL-fetching tools request user-configured or external URLs. According to the maintainers, 1.2.1 is a patch-level release that differs from 1.2.0 only by the upstream decoder correction. Onyx treated the upgrade as critical and backported it to multiple release branches, documenting one maintainer's assessment that the vulnerability is reachable in production. This sequence does not establish a universal fixed version or remediation procedure for all Python deployments.
Next steps
Check the installed brotli version in your deployment environment, trace whether your application decompresses untrusted Brotli data or fetches external URLs through libraries that auto-decode br responses, and consult the PYSEC-2026-4322 advisory for updated remediation guidance once the upstream project confirms the affected and fixed version range.
Verification status: Verified against official documentation; not reproduced in a test environment by IGPROD. Checked 2026-10-24.
Applies to: 1.2.1.
Related advisories
- Pillow FlashPix JPEG heap overflow: another decoder bug in a Python package.
- uv 0.13.4 removes the emSign root CA: another Python tooling update to apply.
Sources:
- Brotli: Out-of-bounds write in the Brotli (github.com)
- Vulnerable dependency: brotli (PyPI) · Issue #16620 · onyx-dot-app/onyx (github.com)
- Vulnerable dependency: brotli (PyPI) on release/v4.8 · Issue #16626 · onyx-dot-app/onyx · GitHub (g…
- Vulnerable dependency: brotli (PyPI) on release/v5.0 · Issue #16629 · onyx-dot-app/onyx (github.com)