A GitHub security advisory reports a heap buffer overflow in Pillow's FlashPix (FPX) JPEG-tile decoder that can lead to arbitrary code execution when an application opens and decodes a crafted file. The advisory demonstrates command execution on Pillow 12.2.0 under specific conditions. A secondary bot-generated report states that versions before 13.0.0 are affected and that 13.0.0 fixes the issue, but the primary advisory excerpt does not document the affected range or a verified fix.
When FPX decoding is exposed
The vulnerability is reachable when two conditions hold: the application opens attacker-influenced files with Pillow's Image.open() and calls .load() to decode them, and the optional olefile dependency is installed. Pillow auto-detects FlashPix files by their OLE2 magic bytes (D0CF11E0...) regardless of file extension, so upload handlers, thumbnailing services, avatar processors, and document conversion pipelines that accept arbitrary uploads are all in scope. No user interaction beyond the upload itself is required.
What a crafted FPX file can trigger
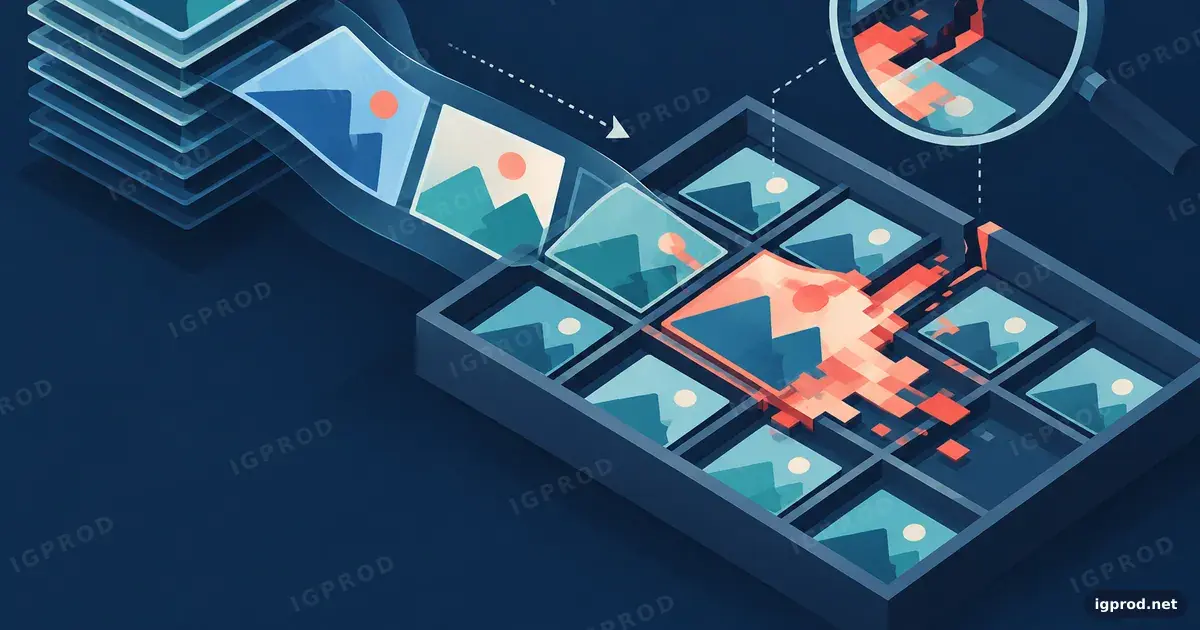
The advisory explains that FpxImagePlugin decodes JPEG-compressed FlashPix subimages by building a decode tile with a raw mode derived from attacker-controlled color IDs. When the plugin selects raw mode LA (two bytes per pixel), Pillow allocates a tile buffer sized for two bytes per pixel. The result is that jpeg_read_scanlines writes four bytes per pixel into a buffer allocated for two, producing a heap out-of-bounds write with attacker-controlled length (the image width, potentially tens of thousands of pixels) and attacker-controlled content (the decoded pixel data).
The advisory states that the overflow can corrupt adjacent heap objects and lead to arbitrary command execution. The supplied proof-of-concept overwrites a Python bytes object's ob_type pointer with a fake vtable planted in the decode buffer, hijacking an indirect call during PyBuffer_Release to execute system() with an attacker-supplied command string.
What the code execution demonstration establishes
The advisory provides a working proof-of-concept that achieves command execution on Pillow 12.2.0 running on x86_64 Ubuntu 24.04 with glibc 2.39, inside a Docker container with ASLR disabled via setarch -R. The PoC uses version-pinned Python 3.12.3 and crafts a standalone .fpx file that, when opened with Image.open() and decoded with .load(), runs id via system() and then crashes during interpreter teardown. The demonstration confirms exploitability under those exact conditions, but the advisory excerpt does not document the affected version range, whether earlier or later Pillow releases are vulnerable, or whether the exploit generalizes to other architectures, distributions, or ASLR-enabled systems.
Version range and fix claims
A bot-generated security issue (GitHub issue #43) states that Pillow versions prior to 13.0.0 are affected and that version 13.0.0 fixes the issue. The primary Pillow security advisory does not verify that range or fix.
Check your deployment for exposure
To assess whether your deployment is exposed, check whether the olefile package is installed in the environment where Pillow runs. In a Python virtual environment or container, run:
pip show olefile
If olefile is present, identify all code paths where untrusted or user-uploaded files reach Image.open() followed by .load(), .save(), thumbnail generation, or any other operation that decodes the image. Upload endpoints, webhook processors, and background jobs that thumbnail or convert images are candidate paths.
Removing the olefile dependency eliminates FlashPix support and closes the documented exposure if FlashPix files are not required. File-extension allow-lists do not mitigate the issue because Pillow detects FlashPix by OLE2 magic bytes in the file content. The advisory does not document whether validating file formats with a separate tool before passing them to Pillow, or running image processing in sandboxed low-privilege containers, effectively contain exploitation; these measures may reduce impact but their sufficiency is not verified.
Until the Pillow project publishes the complete affected version range, a confirmed fixed release, and upgrade instructions, the documented demonstration on 12.2.0 and the bot report's 13.0.0 fix claim remain the only available version signals.
Verification status: Supported by official documentation only under the conditions below; not reproduced in a test environment by IGPROD. Checked 2026-10-24.
Applies to: Pillow 12.2.0.
Conditions:
- The application opens attacker-influenced files with Pillow and has the optional olefile dependency installed.
- The advisory's code execution demonstration uses Pillow 12.2.0 on x86_64 Ubuntu 24.04 with glibc 2.39.
Related advisories
- Brotli decoder vulnerability (Node2Shell) on PyPI: another decoder bug in a Python package.
Sources: